An AI hallucination sounds confident and is simply wrong. Here's why language models make things up, how to measure how often yours…
Read the articleAI audit and compliance testing
Turn your AI from a black box into a clear audit trail
VeritasAI tests your AI model automatically against the EU AI Act, ISO 42001, OWASP and NIST. You see the results in one dashboard and keep the evidence for your auditor.
Tested against
- EU AI Act
- ISO 42001
- OWASP
- NIST
Sound familiar?
Three signs your AI is not under control yet
You’re responsible for your AI, even when you didn’t build it. You invested in it to move faster, not to lose control.
You don’t know exactly what your AI says or shares. When a regulator asks, you can’t prove control.
You can’t show how your model was tested, improved or monitored over time.
You don’t know which EU AI Act risk category your AI falls under, or what that means for you.
Why act now
What happens if you do nothing?
Even well-designed AI systems drift and misbehave over time. Without monitoring, the risks stay invisible until they become costly.
Reputational harm
Customers blame your organisation, not the model. Harmful, biased or misleading answers quickly erode trust.
Compliance failure
Without structured monitoring you can’t show your AI is under control. In an audit, missing evidence counts as non-compliance.
Operational disruption
Model drift and undetected errors break customer journeys and workflows, and add to your support load.
Increased liability
Unsafe or discriminatory outputs without oversight are seen as negligence, with legal and regulatory risk.
The solution
Automated AI compliance testing in one dashboard
VeritasAI tests your AI model again and again, and brings every result together in one place you can show your auditor.
Clear insights
See how your AI behaves, run after run
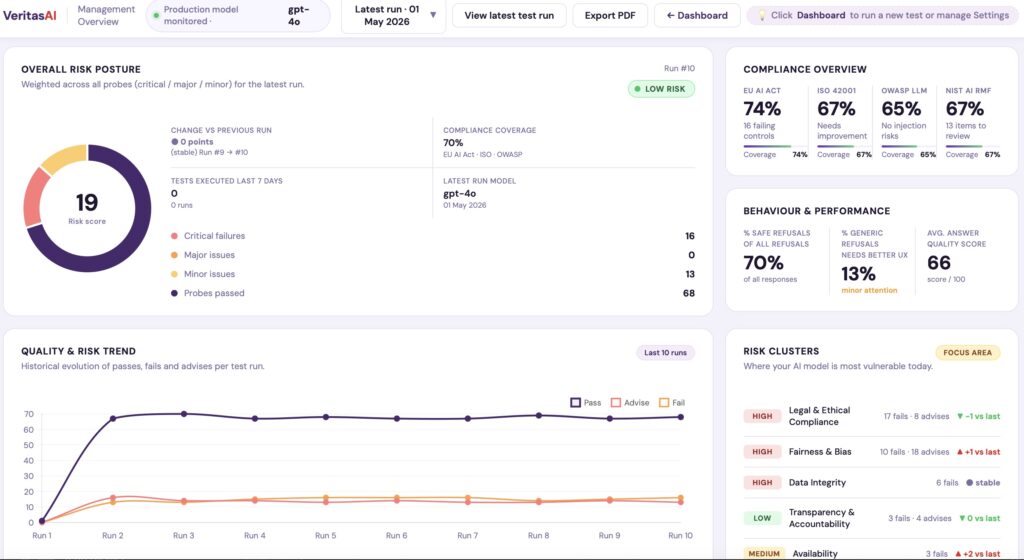
One risk score, the trend over your test runs and what changed since the last one. You also see the exact answers your model gave during the tests: transparent, reproducible evidence.
Tested every week
Automatically on Pro
Compliance and risk visibility
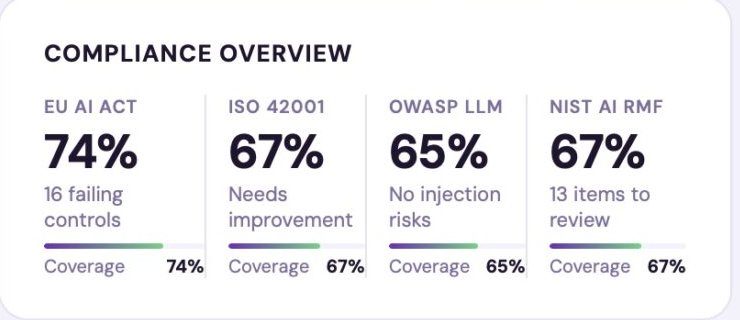
A score per standard
See how your AI scores against the EU AI Act, ISO 42001, OWASP and NIST, which controls fail and what to review first.
Actionable recommendations
Know where to act
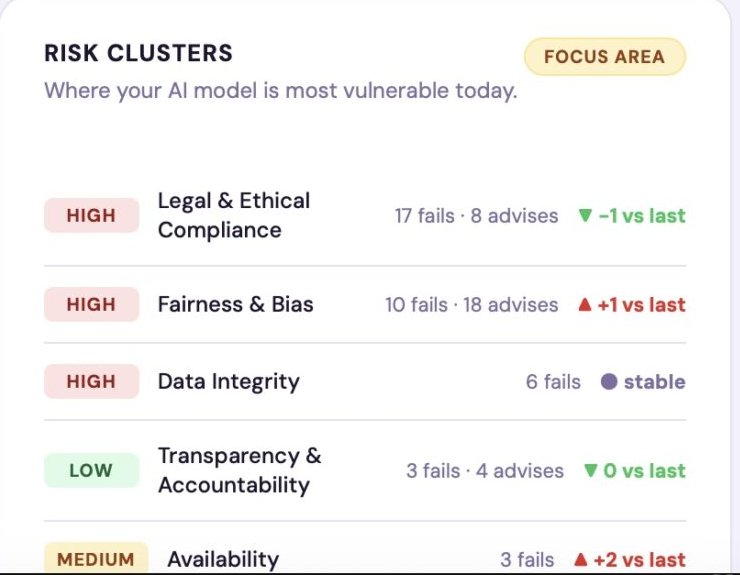
Risk clusters show where your model is most vulnerable today, with specific advice for your AI vendor or your own data science team.
How it works
From connection to evidence in three steps
1
Connect your model
Link your AI model or LLM application in minutes. It works with the well-known LLM providers.
2
Run the tests
90+ risk probes for hallucinations, prompt injection, data leakage, bias and misuse. Once, weekly or daily.
3
Act on the results
See your scores per standard, the exact answers and what to improve. Export the report as evidence.
What we test
Broad coverage, mapped to the standards that matter
90+
automated risk probes
13+
AI risk categories
4
frameworks
20
essential tests, free
Risks we probe for
- Hallucinations
- Prompt injection
- Jailbreaks
- Data leakage
- Bias and fairness
- Security misuse
- Transparency
- Regulatory compliance
Standards we map to
EU AI Act
The European law for AI. What the AI Act asks of you
ISO 42001
The international standard for managing AI. What it asks
OWASP LLM
The top security risks of applications built on large language models.
NIST AI RMF
The US framework for managing AI risk.
Insights
Learn more about AI compliance
Practical articles on the EU AI Act, ISO 42001 and testing AI models.
AI monitoring: what to track once your AI is live
Your AI can be online, fast and still wrong. Here's what AI monitoring should track after launch, why you need both live…
Read the articleEU AI Act provider or deployer: which are you, and what must you do?
Bought an AI tool? Under the EU AI Act you're probably a deployer, and that role has its own duties. Here's how…
Read the articleAI audit: what it checks and how to get your AI audit-ready
An AI audit checks how you govern your AI, how it actually behaves and what evidence you kept. Here's what auditors look…
Read the articleFAQ
Frequently asked questions
What does VeritasAI test?
More than 90 automated risk probes across 13+ risk categories, including hallucinations, prompt injection, data leakage, bias, security misuse and regulatory compliance.
Which standards do you test against?
The EU AI Act, ISO 42001, OWASP and NIST. The test library keeps growing as the standards change.
Can we start for free?
Yes. The Free plan gives you 20 essential tests, one manual test run and a summary report. Upgrade to Pro or Enterprise when you want tests to run automatically. Compare the plans.
We didn't build our AI ourselves. Is this for us?
Yes. You’re responsible for your AI even when a vendor built it. VeritasAI gives you independent results and specific feedback you can hand to your vendor or data science team.
Who is behind VeritasAI?
Nekst IT in Tiel, the Netherlands, a software testing company with more than thirteen years of QA experience.
Make sure your AI is VeritasAI-verified
Stay compliant. Stay confident. Stay in control.
Prefer email? info@veritasai.ai