EU AI Act compliance
The EU AI Act: what your organisation must do
A practical guide to the EU AI Act: which rules apply to your AI, when they start and how you show that you comply.
In short
What is the EU AI Act?
The EU AI Act, Regulation (EU) 2024/1689, is the European law for artificial intelligence. It applies to everyone who places AI systems on the EU market or uses them in the EU, also when the company is based outside the EU.
The rules depend on the risk. The more harm an AI system could do to health, safety or fundamental rights, the stricter the requirements. For most organisations it comes down to three questions: which risk category is our AI in, what is our role, and can we show that we comply?
Risk categories
Four levels of risk
Your duties depend on what your AI is used for, not on the technology. Read how to find your AI’s category.
Unacceptable risk
Banned. For example social scoring and emotion recognition at work or at school.
High risk
Allowed with strict requirements: risk management, testing, documentation, logging and human oversight. For example AI for hiring, credit scoring or exams.
Limited risk
Transparency duty: people must know they are dealing with AI, for example a chatbot or AI-generated images.
Minimal risk
No new duties under the AI Act, such as spam filters or AI in games. Other laws, such as the GDPR, still apply.
Your role
Provider or deployer: your duties differ
Provider
You develop an AI system, or have it developed, and place it on the market under your own name. For high-risk systems you carry the heaviest duties: risk management, technical documentation, conformity assessment and post-market monitoring.
Deployer
You use an AI system in your organisation, also when a vendor built it. For high-risk systems you use it according to the instructions, arrange human oversight, monitor how it works and keep the logs.
Everyone
Since 2 February 2025 every organisation that uses AI must make sure its staff have sufficient AI literacy: they understand what the AI does, what the risks are and how to work with it responsibly.
Timeline
When do the rules apply?
1 August 2024
The AI Act enters into force.
2 February 2025
The bans on prohibited AI practices apply, and so does the AI literacy duty.
2 August 2025
Rules for general-purpose AI models, such as large language models.
2 August 2026
Most other rules, including the transparency duties and the requirements for high-risk systems in Annex III.
2 August 2027
Requirements for high-risk AI in products already covered by EU product legislation.
In November 2025 the European Commission proposed to postpone part of the high-risk rules (the Digital Omnibus package). Always check the current dates on the European Commission’s website before you plan.
Fines
What is at stake?
- Up to €35 million or 7% of worldwide annual turnover for prohibited AI practices
- Up to €15 million or 3% for breaching most other obligations
- Up to €7.5 million or 1% for giving incorrect or misleading information to authorities
For SMEs and start-ups the lower of the two amounts applies. Besides fines, an authority can also require you to change a system or take it out of use.
Get started
How to get your organisation AI Act-ready
Six steps that work for almost every organisation, whether you build your AI or buy it.
1
Map your AI
List every AI system you build or use, bought tools included: what does it do and who does it affect?
2
Set category and role
For each system, pick the risk category and whether you are provider or deployer. Write down why in a few sentences. Help with the risk category.
3
Test it and prove it
Test your AI for the risks that come with its category: hallucinations, bias, data leakage and prompt injection. Keep the results as evidence.
4
Keep monitoring
AI changes after launch, even when nobody touches the code. So test again regularly. Read about model drift.
5
Set up governance
Record responsibilities, human oversight and documentation. ISO 42001 gives you a useful framework.
6
Train your people
Build AI literacy: staff who work with AI must understand what it can do and what the risks are.
Evidence for the AI Act
How VeritasAI helps
VeritasAI tests your AI model automatically with 90+ risk probes across 13+ categories, mapped to the EU AI Act, ISO 42001, OWASP and NIST. You see how your AI scores per standard, which answers the model gave and what to improve. With weekly tests you build up the evidence an auditor asks for.
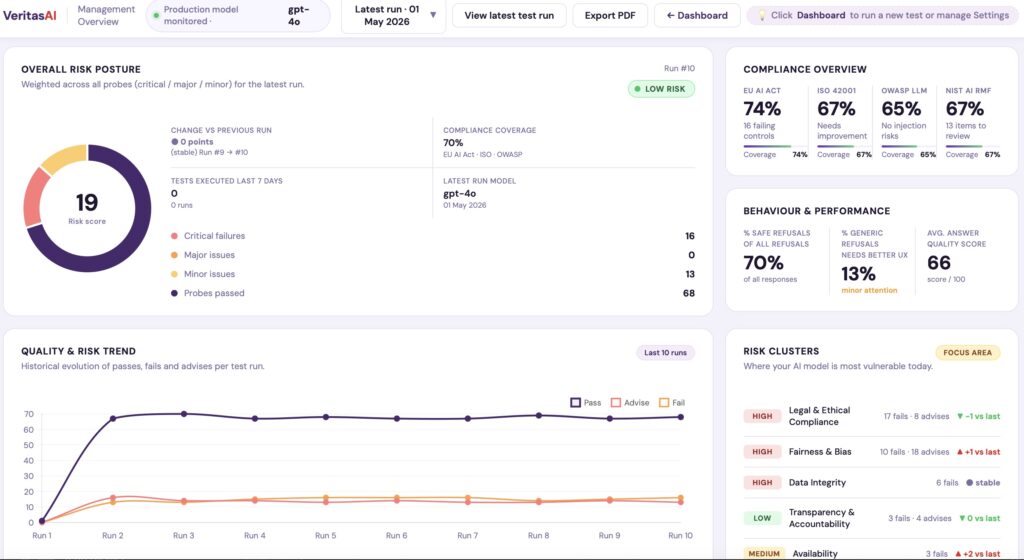
VeritasAI does not give legal advice and is not a certification. It does give you the test evidence you need to show that your AI is under control.
FAQ
Frequently asked questions about the EU AI Act
Does the AI Act apply to us if we only use AI?
Yes. Also when you buy AI and only use it, you have duties. AI literacy applies to everyone. If you use a high-risk system, you must use it according to the instructions, arrange human oversight, monitor how it works and keep the logs.
Is ChatGPT high risk under the AI Act?
The underlying model falls under the rules for general-purpose AI models, which mainly apply to its maker. Your use of it gets its own category: as a writing aid usually minimal risk, for screening job applicants high risk.
What is the difference between the AI Act and ISO 42001?
The AI Act is law: you must comply. ISO 42001 is a voluntary standard for managing AI in your organisation. It does help you meet many AI Act requirements in a way you can show.
Does the AI Act apply to companies outside the EU?
Yes, if the AI system is placed on the EU market or its output is used in the EU. Where the company is based does not matter.
How do you show that your AI complies?
With documentation and evidence over time: how the system was tested, what went wrong and what you improved. A one-off check is not enough; testing regularly and keeping the results is.
Make sure your AI is VeritasAI-verified
Stay compliant. Stay confident. Stay in control.
Prefer email? info@veritasai.ai